How to integrate APIs seamlessly
Build resilient API integrations from the start. Handle authentication, rate limits, and edge cases before they break production.
API integration failures cost hours you can't afford. Authentication tokens expire during critical workflows, triggering 401 errors that cascade through your services. Rate limits silently throttle requests, causing timeout failures downstream. Schema changes in third-party APIs break production integrations without warning.
Most teams debug the same way: code up the implementation, ship to production, then retrofit error handling after failures emerge. By the time you're parsing 429 responses and handling token refresh loops, you're already firefighting instead of building.
Traditional integration approaches work, but they require extensive trial-and-error cycles to discover failure modes that could be anticipated upfront. Here's how to shift from reactive debugging to systematic integration planning.
How most API integration actually happens
Parse documentation and identify edge cases
API integration typically starts with optimistic assumptions based on documentation. You implement authentication flows, handle successful responses, and process expected payloads. Edge cases emerge only after production failures reveal the gaps.
This approach works for simple integrations with forgiving APIs. But production reveals undocumented behaviors: rate limits that vary by endpoint, authentication headers that expire mid-request, or webhook retries that arrive out of order. By the time you discover these patterns, users are already experiencing failures.
Debug through trial and error
You discover each failure mode through production incidents, then implement fixes reactively. Rate limits hit during peak traffic, so you add backoff logic. Tokens expire mid-request, so you implement refresh handling. Each API vendor implements these patterns differently, so reproducing the exact conditions that triggered each problem becomes its own debugging challenge.
Build error handling manually
Building robust error handling happens through painful iteration. The first retry mechanism is too aggressive, creating cascade failures. The backoff strategy needs tuning after discovering that all clients retry simultaneously during outages.
Production experience accumulates slowly across multiple API integrations. Each vendor implements rate limiting differently—some count by user, others by IP, some by API key. This knowledge gets built through months of debugging specific failure patterns rather than upfront design.
Collaborate API integration with Claude
You can integrate AI coding assistants like Claude into your integration workflows to design resilient architectures before writing code. Identify failure modes during planning, validate authentication strategies, and build comprehensive error handling from the start rather than retrofitting after production incidents.
You can work with Claude in two different ways:
Claude.ai provides a free web interface where you can paste API specifications, explore authentication flows, and receive integration guidance with specific failure scenarios to prevent. Accessible from any browser, desktop, or mobile device.
Claude Code integrates directly into your development environment as an agentic terminal tool. It autonomously analyzes entire codebases, generates production-ready clients with comprehensive error handling, and implements authentication flows that match your existing patterns.
Start with Claude.ai
Before writing integration code or setting up testing environments, you can validate your understanding of an API's requirements and potential pitfalls. This upfront analysis helps you identify authentication flows, error scenarios, and rate limiting strategies upfront, reducing the need for post-implementation debugging. Some common integration questions you might ask Claude:
- "Here's a Stripe webhook signature error. What validation steps am I missing?"
- "Why might OAuth tokens expire during multi-step checkout flows?"
- "Compare webhook vs polling for real-time inventory updates"
This immediate feedback supports making informed integration decisions during development rather than discovering issues through production incidents.
Identify failure modes before implementation
Before writing integration code, Claude helps you think through potential issues systematically. Ask Claude to identify scenarios that trigger specific errors: timeouts, rate limiting, authentication failures.
Example: "What could break with this payment API during high traffic? Include rate limiting and timeout scenarios."
Claude outlines common culprits like token expiration windows, connection pooling limits, idempotency requirements. Get a focused set of issues to prevent instead of discovering through production failures.
Transform specifications into action items
Use the web search feature or paste API documentation into Claude. Ask for "integration risks ranked by likelihood."
Claude identifies patterns in specifications, highlighting specific issues: rate limit thresholds, required headers, field-level nullability. Instead of "implement error handling," your team gets "add exponential backoff for 429 responses with jitter to prevent thundering herd."
Scale up with Claude Code for complex integrations
When integrations span multiple services or require comprehensive error handling across your codebase, Claude Code automatically analyzes your entire codebase, implements authentication flows, and helps users ship production-ready clients.
Install:
npm install -g @anthropic-ai/claude-codeLaunch in your project:
claudeStart integrating APIs with Claude:
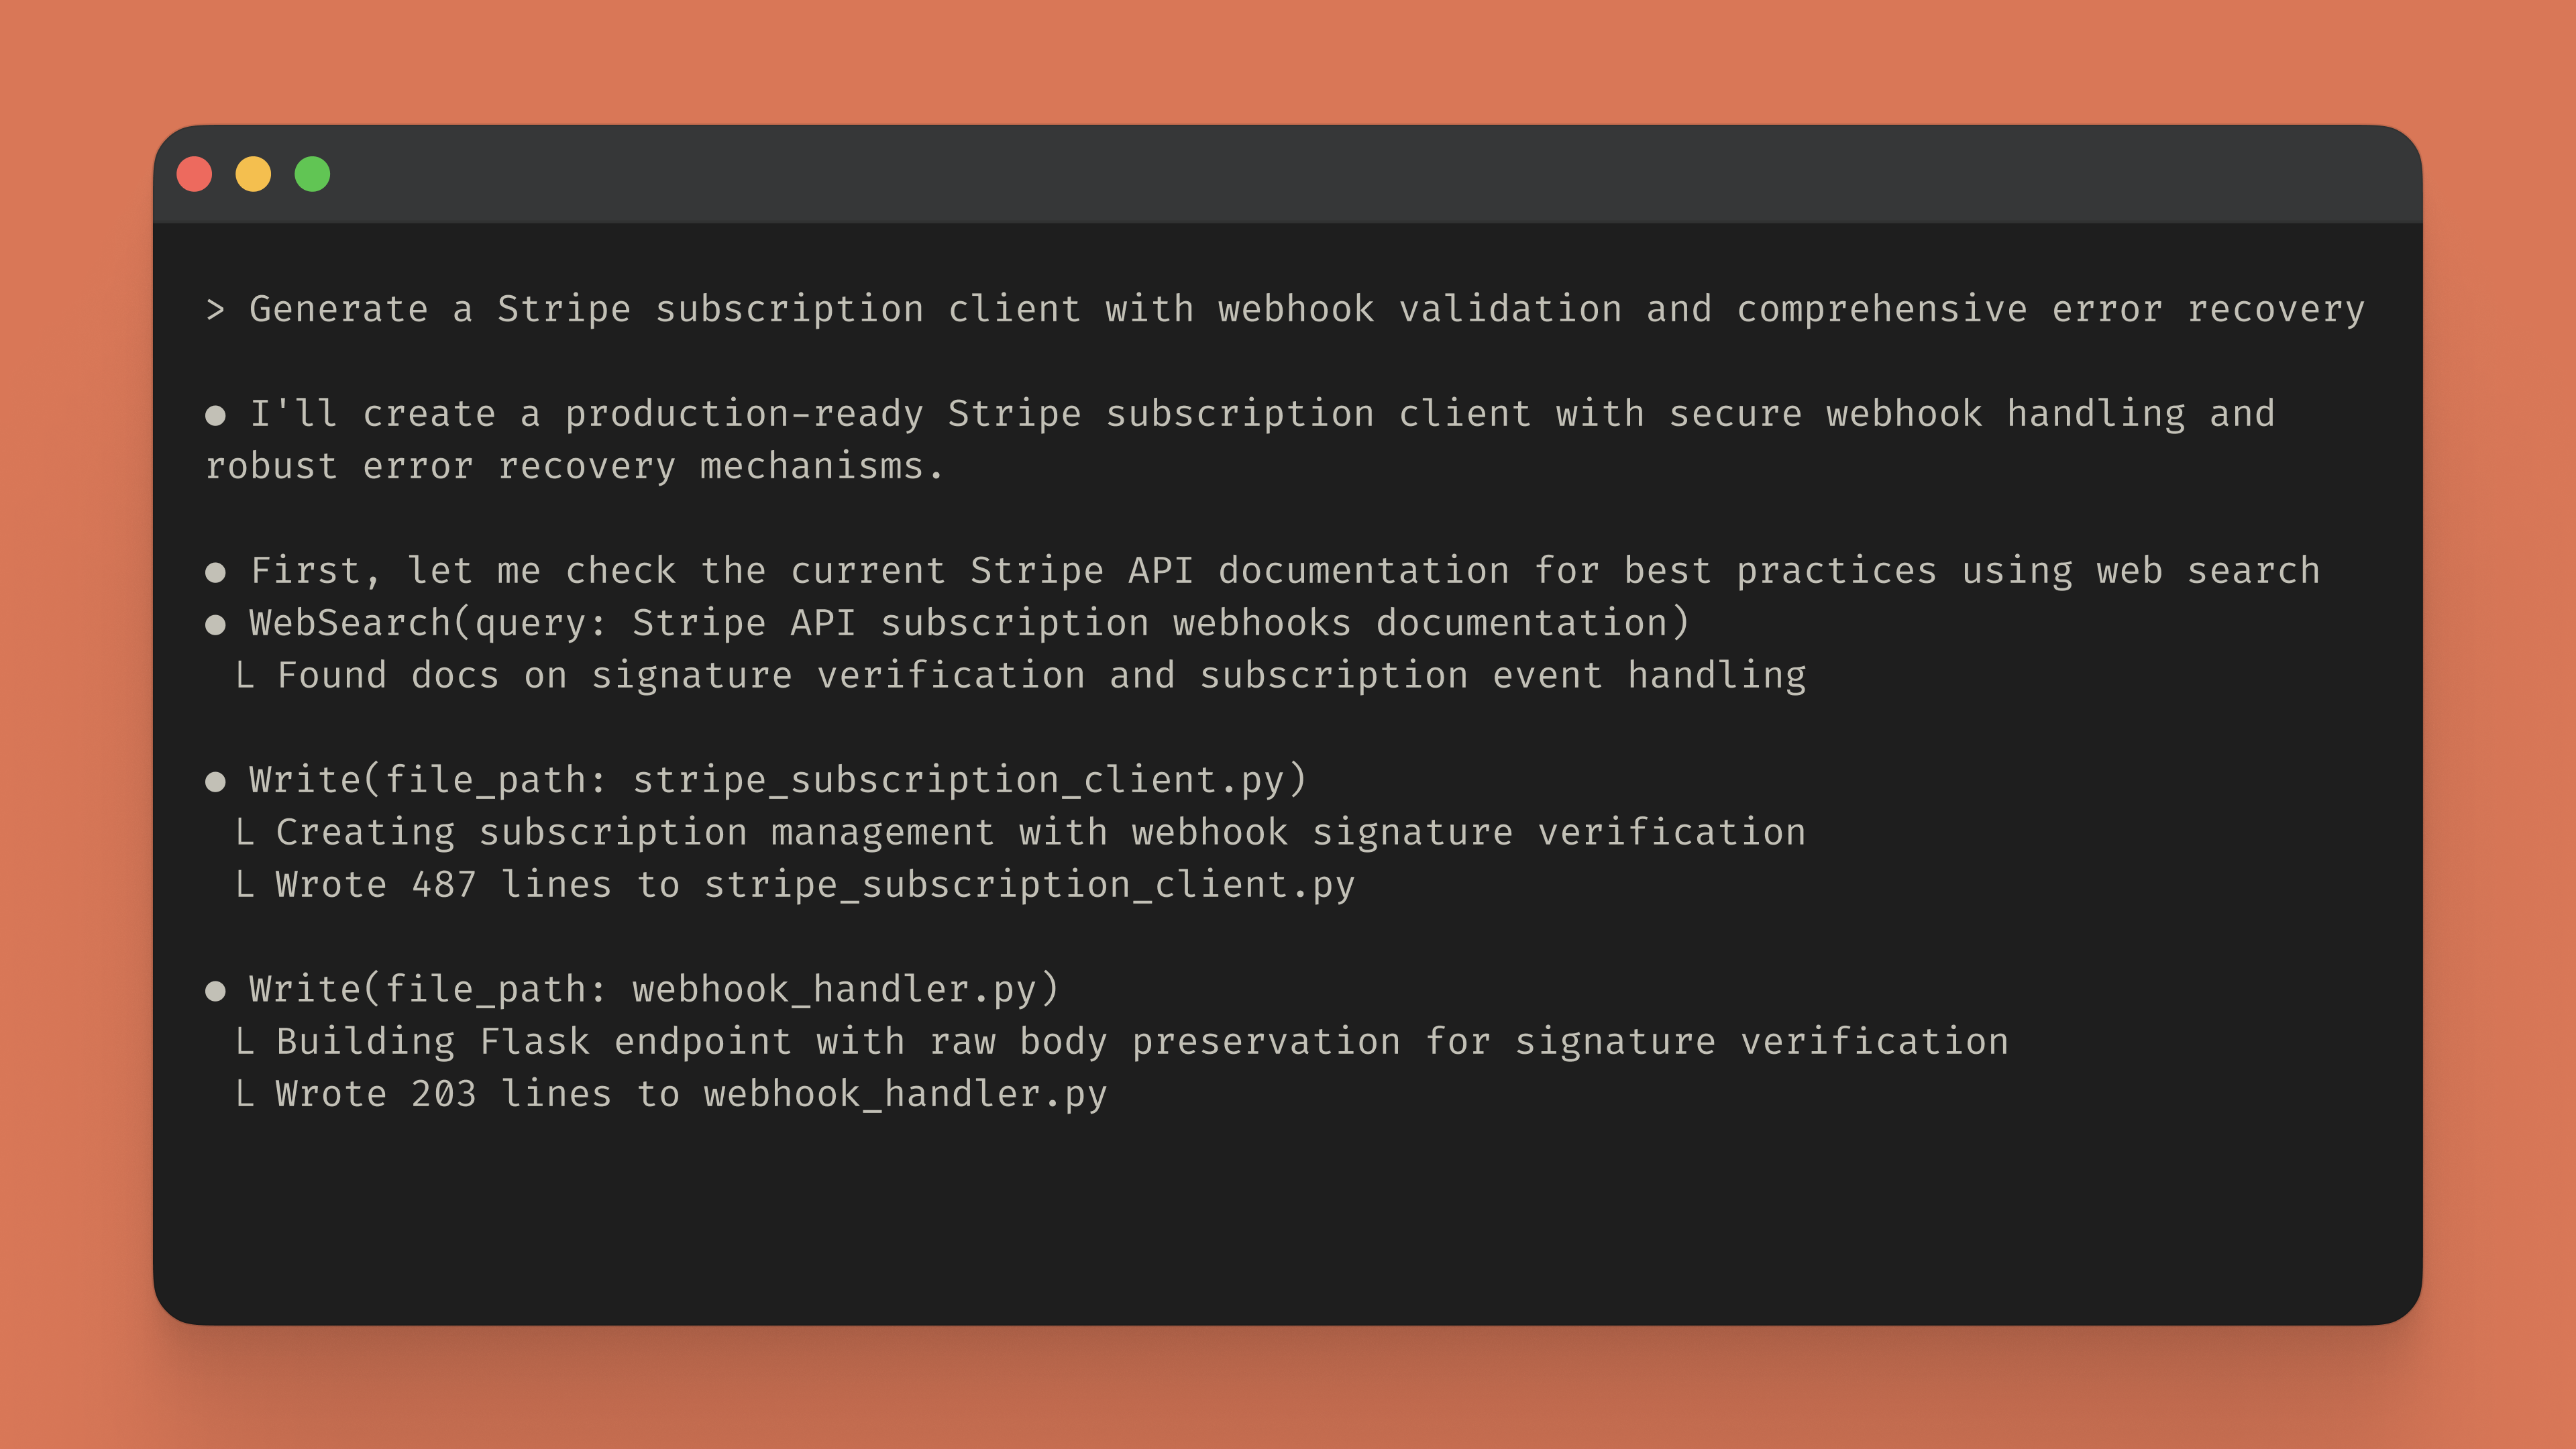
Claude Code analyzes API specifications, creates typed clients matching your project patterns, implements retry mechanisms with your existing utilities. You reduce initial integration time by preventing common failure modes during implementation rather than discovering them in production.
Implement authentication systematically
Some integrations require complex authentication flows. Claude Code handles OAuth2, JWT validation, and API key rotation without hardcoded credentials:
- "Build OAuth2 flow for Google Calendar with automatic token refresh"
- "Create rotating API key system for Twilio with monitoring"
- "Implement JWT validation for microservices"
Claude Code can suggest implementations using environment variables and integration patterns that match your existing secret management approach.
Validate with comprehensive tests
Once implemented, ask Claude to generate and run tests verifying that the integrations handle edge cases properly:
- "Create tests that reproduce this rate limit scenario"
- "Generate contract tests for schema validation”
- "Run tests for authentication refresh during long operations"
Ship with automated workflows
After tests pass, Claude Code handles the release process:
> Commit these API changes and open a PRGenerates descriptive commit messages, crafts clear PR descriptions linking changes and test coverage.
Choose your integration approach
Claude.ai: to evaluate new APIs, understand authentication requirements, or plan error handling strategies before implementation. The browser interface supports sharing integration approaches with your team or conducting research about vendor-specific API behaviors via web search functionality.
Claude Code: Use Claude Code when you need to generate boilerplate client code, implement complex authentication flows across multiple files, or create comprehensive test suites. The agentic terminal integration is essential for implementations that touch configuration files, environment variables, and CI/CD pipelines.
Describe the integration you're trying to build, and Claude Code generates clients with proper error handling and production-ready authentication flows.
FAQ
Analyzing API documentation upfront helps identify rate limit thresholds, counting methods (per user, per IP, per API key), and reset windows before deployment. AI tools like Claude analyze specifications to suggest appropriate backoff strategies, request queuing patterns, and circuit breaker implementations based on your specific API requirements. This prevents the trial-and-error cycle of discovering rate limits through production failures.
Paste the API documentation into Claude.ai and ask specific questions about the authentication requirements. Claude breaks down OAuth2 flows, token refresh cycles, and header requirements in plain language. You get concrete implementation guidance for handling token expiration, refresh logic, and credential rotation without parsing through pages of vendor documentation.
The choice depends on your latency requirements, data volume, and infrastructure constraints. Webhooks provide immediate updates but require webhook validation, idempotency handling, and retry logic for failed deliveries. Polling offers simpler implementation but increases API calls and introduces latency. Claude can analyze your specific use case and API constraints to recommend the approach that fits your requirements, including hybrid strategies that combine both methods.
Implement versioned clients that support multiple API versions simultaneously, use schema validation to catch breaking changes early, and create adapter layers that translate between old and new response formats. Claude Code can analyze schema differences between API versions and generate migration code that maintains backward compatibility during transition periods.